User Management & Role-Based Access Control (RBAC)
This guide details the multi-user authentication system and Role-Based Access Control (RBAC) integrated into Gluesync CoreHub. It outlines the available roles, permissions, password policies, and API usage for user management.
|
How-to guides
For step-by-step walkthroughs tested on a running Gluesync, see the how-to guides Manage users, groups, and roles and Configure SSO with OIDC and map roles. |
Overview
Gluesync CoreHub supports a robust multi-user environment. It allows administrators to create multiple accounts, assign distinct roles for varied permission levels, and manage overall platform security through specific access controls.
|
If you are looking to integrate an external identity provider to manage your users via Single Sign-On, see Configure OIDC Authentication. |
User Roles
The system supports four user roles that you can assign to people. A fifth role, EXTERNAL_MODULE, is used internally by Gluesync modules such as Chronos and is never assigned to a person.
1. SUPER ADMIN (formerly "admin")
-
Full system access.
-
Can create, update, and delete users with any role, and manage user groups and Query data access rules.
-
Can perform all operational, configuration, and structural changes.
-
Cannot be deleted. (The default
adminuser retains this role.) -
Can reveal unmasked PII in Query Studio and can disable platform-wide PII masking under Settings → Global settings. See PII discovery and masking.
2. MANAGER
-
Can perform all system operations except managing Super Admin accounts, user groups, and Query data access rules.
-
Can create, modify, and delete pipelines and entities.
-
Can start, stop, and pause replications.
-
Can create, update, and delete
MANAGERandVIEWERusers, in Settings → Users & access or with the user management API. Cannot create, change, or delete aSUPER ADMINorMONITORuser. -
Cannot delete the primary admin user.
-
Can reveal unmasked PII in Query Studio for a single session. Cannot change the platform-wide masking setting.
3. MONITOR
-
For operators who run replications but must not build or delete anything.
-
Can start, stop, and pause replications and run snapshots.
-
Can modify the settings of existing entities.
-
Can save personal queries in Query Studio and see the pipeline and team queries shared with them.
-
Cannot create or delete pipelines, entities, connections, or agents.
-
Cannot change global settings or manage users.
-
Cannot run writable queries, share saved queries, or reveal unmasked PII in Query Studio.
-
Not offered in the Control Plane role list: a
SUPER ADMINassigns it with the user management API ("role": "MONITOR"), and OIDC role mappings toMONITORare set with the API too. See Manage users, groups, and roles.
4. VIEWER
-
Read-only access to all resources.
-
Can view pipelines, entities, metrics, and logs.
-
Can run read-only queries in Query Studio.
-
Cannot make any modifications.
-
Cannot pause, start, or stop replications.
-
Cannot create, update, or delete any resources.
-
Cannot save, share, or run writable queries in Query Studio.
-
Cannot reveal unmasked PII in Query Studio. See PII discovery and masking.
For a side-by-side comparison, including the Settings sections each role sees, see Compare the roles.
Authentication & Security
Password Requirements
All passwords must meet the following criteria to ensure system security: * Minimum of 8 characters * At least 1 lowercase letter * At least 1 uppercase letter * At least 1 special symbol
First Login & Temporary Passwords
When a SUPER ADMIN or a MANAGER creates a new user or resets a user’s password, the account is flagged to mandate a password change. This means the user must change their temporary password upon their very first login before accessing any other CoreHub endpoints or UI features.
Personal API Tokens
Scripts, AI assistants, and BI tools authenticate with Personal API Tokens (gsp_…) instead of a password. A token never has more access than its user’s role, and its permission and agent scopes narrow it further. See Personal API Tokens and scopes.
Session Management
User sessions are managed through JWT (JSON Web Tokens). By default, sessions expire after 72 hours. A SUPER ADMIN can change this value from the Settings → Users & access panel. See Session Configuration.
Managing Users via the Web UI
The Settings → Users & access tab provides a full graphical interface for managing accounts. SUPER ADMIN and MANAGER users can open it; a MANAGER acts only on MANAGER and VIEWER accounts, and only a SUPER ADMIN sees User groups and OIDC configuration.
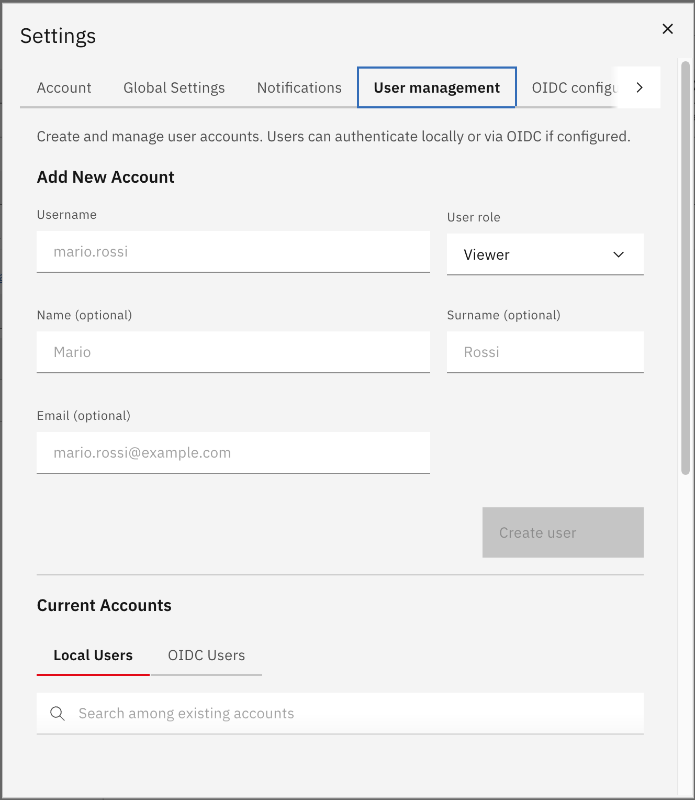
Creating a New User
-
Open Settings → Users & access.
-
Fill in the Add New Account form:
-
Username (required) — must be unique; logins are case-insensitive.
-
Role — select
MANAGERorVIEWER.SUPER ADMINandMONITORcan only be assigned via the REST API. -
Name, Surname, Email — optional display fields.
-
-
Click Create.
Gluesync automatically generates a secure random password and displays it once after creation. You can:
-
Copy the password to the clipboard.
-
Download a CSV file containing the username, password, role, and contact fields.
|
Save or share the password immediately — it is shown only once. The user will be required to change it on first login. |
Viewing and Searching Users
The user list is split into two tabs:
-
Local Users — accounts created directly in Gluesync.
-
OIDC Users — accounts auto-provisioned on first OIDC login.
Use the search box to filter by username across the active tab.
Each user row displays:
-
Username
-
Current role
-
OIDCbadge — if the account was provisioned by an identity provider. -
Password Change Requiredbadge — if the user has not yet changed their temporary password.
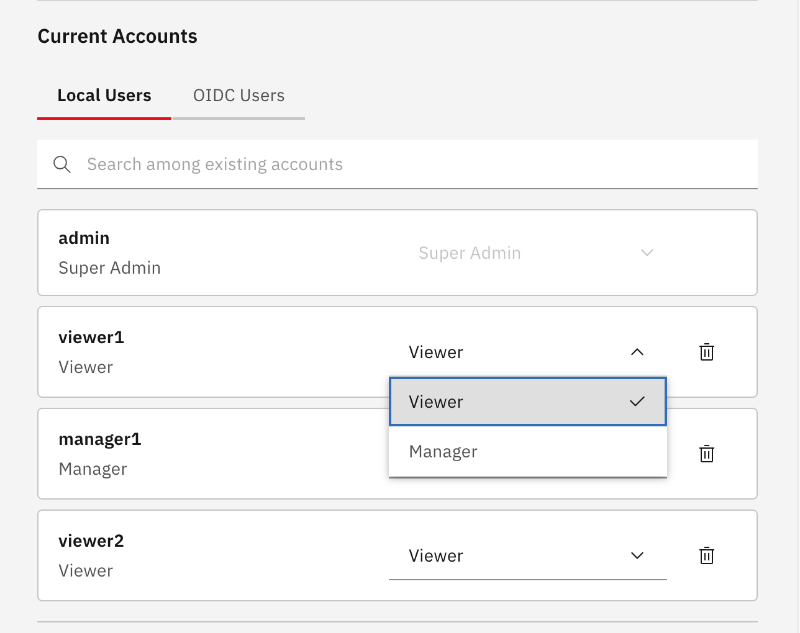
Changing a User’s Role
Select a new role from the dropdown in the user’s row. The change takes effect immediately.
|
Deleting a User
Click the trash icon in the user’s row and confirm the deletion in the dialog.
-
The default
adminaccount cannot be deleted. -
A user cannot delete their own account.
-
OIDC users cannot be deleted via the UI (they are managed by the identity provider).
Self-protection rules
To prevent administrators from accidentally locking themselves out, CoreHub enforces the following self-protection rules on user-management endpoints:
-
A user cannot delete their own account.
-
A user cannot change their own role. All other self-edits (name, surname, email, password) work normally. Requests that attempt to change the caller’s own role return HTTP
400 Bad Requestwith the messageCannot change your own role.
A SUPER ADMIN who needs to demote themselves must have another SUPER ADMIN perform the change.
Session Configuration
Session duration controls how long a login remains valid before the user must authenticate again.
Configuring via the Web UI
-
Open Settings → Users & access.
-
Scroll to the Session Configuration section at the bottom of the page.
-
Enter the desired duration in the Session Duration (Hours) field (minimum: 1 hour; default: 72 hours).
-
Click Save.
The new duration applies to all future sessions. Existing sessions are not immediately invalidated.
|
Only |
API Reference (User Management)
User management APIs are restricted to users holding the SUPER ADMIN or MANAGER role. The two roles differ in scope:
-
SUPER ADMINcan create, update, and delete users with any role. -
MANAGERcan create, update, and delete users with theMANAGERorVIEWERrole only. Attempting to act on aSUPER ADMINorMONITORuser, or to assign one of those roles, returns HTTP403 Forbidden.
In addition, the self-protection rules apply to both roles: nobody can delete their own account or change their own role.
Get All Users
GET /users
Authorization: Bearer <token>
Response Example:
[
  {
    "username": "admin",
    "role": "SUPER_ADMIN",
    "changeRequired": false
  },
  {
    "username": "john.doe",
    "role": "MANAGER",
    "changeRequired": true
  }
]
Create User
Creates a new user and automatically requires them to change their password upon their first login.
POST /users
Authorization: Bearer <token>
Content-Type: application/json

{
  "username": "new.user",
  "password": "TempPass123!",
  "role": "MANAGER"
}
Update User
Both role and password are optional. If a new password is provided by the admin, the user will be forced to change it on their next login.
PUT /users/{username}
Authorization: Bearer <token>
Content-Type: application/json

{
  "role": "MANAGER",
  "password": "NewPassword123!"
}
Delete User
DELETE /users/{username}
Authorization: Bearer <token>
Note: You cannot delete the default admin user, nor can you delete your own user account. See Self-protection rules.
Integration with OIDC (OpenID Connect)
The RBAC system has been designed to work seamlessly with external identity providers. You can map groups and roles from an external Identity Provider (like Keycloak, Entra ID, or Okta) directly to the CoreHub roles (SUPER_ADMIN, MANAGER, MONITOR, VIEWER). The Control Plane form offers MANAGER and VIEWER; map the other roles with the API, as described in Configure SSO with OIDC and map roles.
To learn more about setting up external identity providers, user auto-provisioning, and role mapping, check out the OIDC Integration Guide.